UP ATS Seeks Block on 20 Lakh Fake Email Accounts Linked to Hoax Bomb Threats
November 14, 2026Cyber Probe Uncovers Massive Fake Email Network in Kanpur
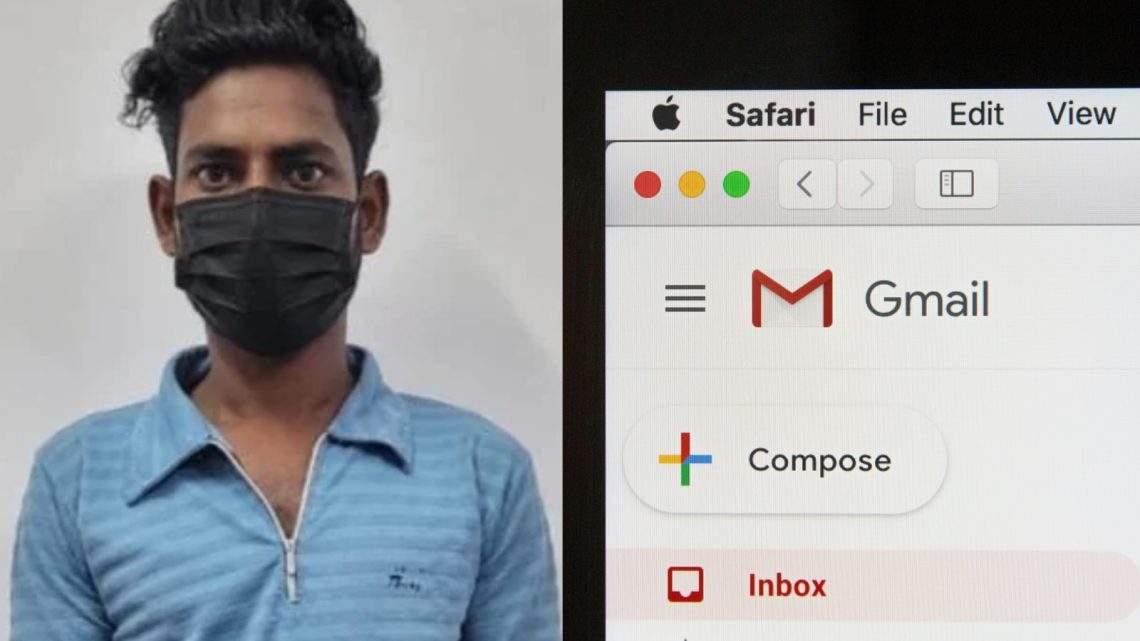
The Uttar Pradesh Anti Terrorism Squad has formally approached Google requesting the immediate blocking of more than 20 lakh fake email accounts linked to a large scale digital fraud and bomb threat investigation. The case centers on Ankit Shankhwar, a 24 year old resident of Ghatampur in Kanpur Nagar, who was arrested on October 28, 2026, after technical tracing linked an email address used in hoax bomb threats back to his location. During the arrest, investigators seized a mobile phone and a second hand laptop containing extensive spreadsheets, recovery passwords, and cryptocurrency wallets. Initial forensic scrutiny of the devices revealed details of nearly five lakh email identities, while deeper analysis uncovered over 20 lakh accounts generated and circulated since 2021.
Hoax Threats Disrupt Schools, Courts, and Public Events
According to official police disclosures, several email accounts generated through this Kanpur based operation were used to send hoax bomb threats to schools, municipal offices, courts, and high profile public gatherings. Investigators linked one specific account discovered on the seized laptop to an October 23 threat sent to the Mumbai Mayor office. Other threatening emails targeted a concert venue in Indore and judicial complexes, spreading widespread panic and forcing emergency evacuations. Security agencies reported that some threat messages falsely invoked banned militant outfits to maximize public alarm and complicate law enforcement attribution. By masking their real locations behind anonymous accounts bought online, perpetrators were able to repeatedly disrupt civic life and drain emergency response resources.
Cryptocurrency Sales and Cross Border Digital Buyers
Forensic examination of the accused suspect devices revealed that the fake email operation functioned as a commercial underground enterprise. Investigators stated that the accused created accounts using public WiFi networks and proxy servers to bypass automated verification checks, while also purchasing existing accounts and resetting their credentials for resale. These bulk digital identities were allegedly advertised and traded through social media groups and encrypted messaging platforms. Buyers paid for the accounts using cryptocurrency, including substantial transfers in USDT, to avoid traditional banking trails. According to the Anti Terrorism Squad, digital communication records and foreign phone numbers found during the probe suggest alleged links with buyers in multiple countries, including Bangladesh, Pakistan, Turkey, and Egypt, though investigators note these cross border buyer connections remain under active verification.
Serious Questions Over Platform Security and Cyber Policing
The discovery that a single operator could generate and trade more than 20 lakh fraudulent email accounts over five years raises serious questions about digital platform safeguards and cybercrime detection. Technology experts note that automated account creation using proxy networks exploits gaps in identity verification systems, allowing malicious actors to stockpile thousands of disposable identities before security algorithms flag suspicious behavior. At the same time, the prolonged duration of the scheme highlights challenges faced by domestic law enforcement agencies in monitoring dark web forums, social media marketplaces, and cryptocurrency transactions. When anonymous digital accounts can be purchased within minutes to issue mass bomb threats, public institutions remain vulnerable to recurring security scares and operational paralysis.
Strengthening Digital Accountability and Preventive Monitoring
Preventing similar large scale cyber exploits requires coordinated action between global technology platforms, financial watchdogs, and national security agencies. Technology companies must deploy stricter behavioral detection tools to identify bulk account farming and rapidly suspend compromised or synthetic identities before they are weaponized. Simultaneously, law enforcement bodies need upgraded forensic capabilities to trace cryptocurrency payments and collaborate across international jurisdictions when digital threats cross borders. Without stronger preventive monitoring and platform accountability, underground markets for fake identities will continue to undermine public safety and digital trust.